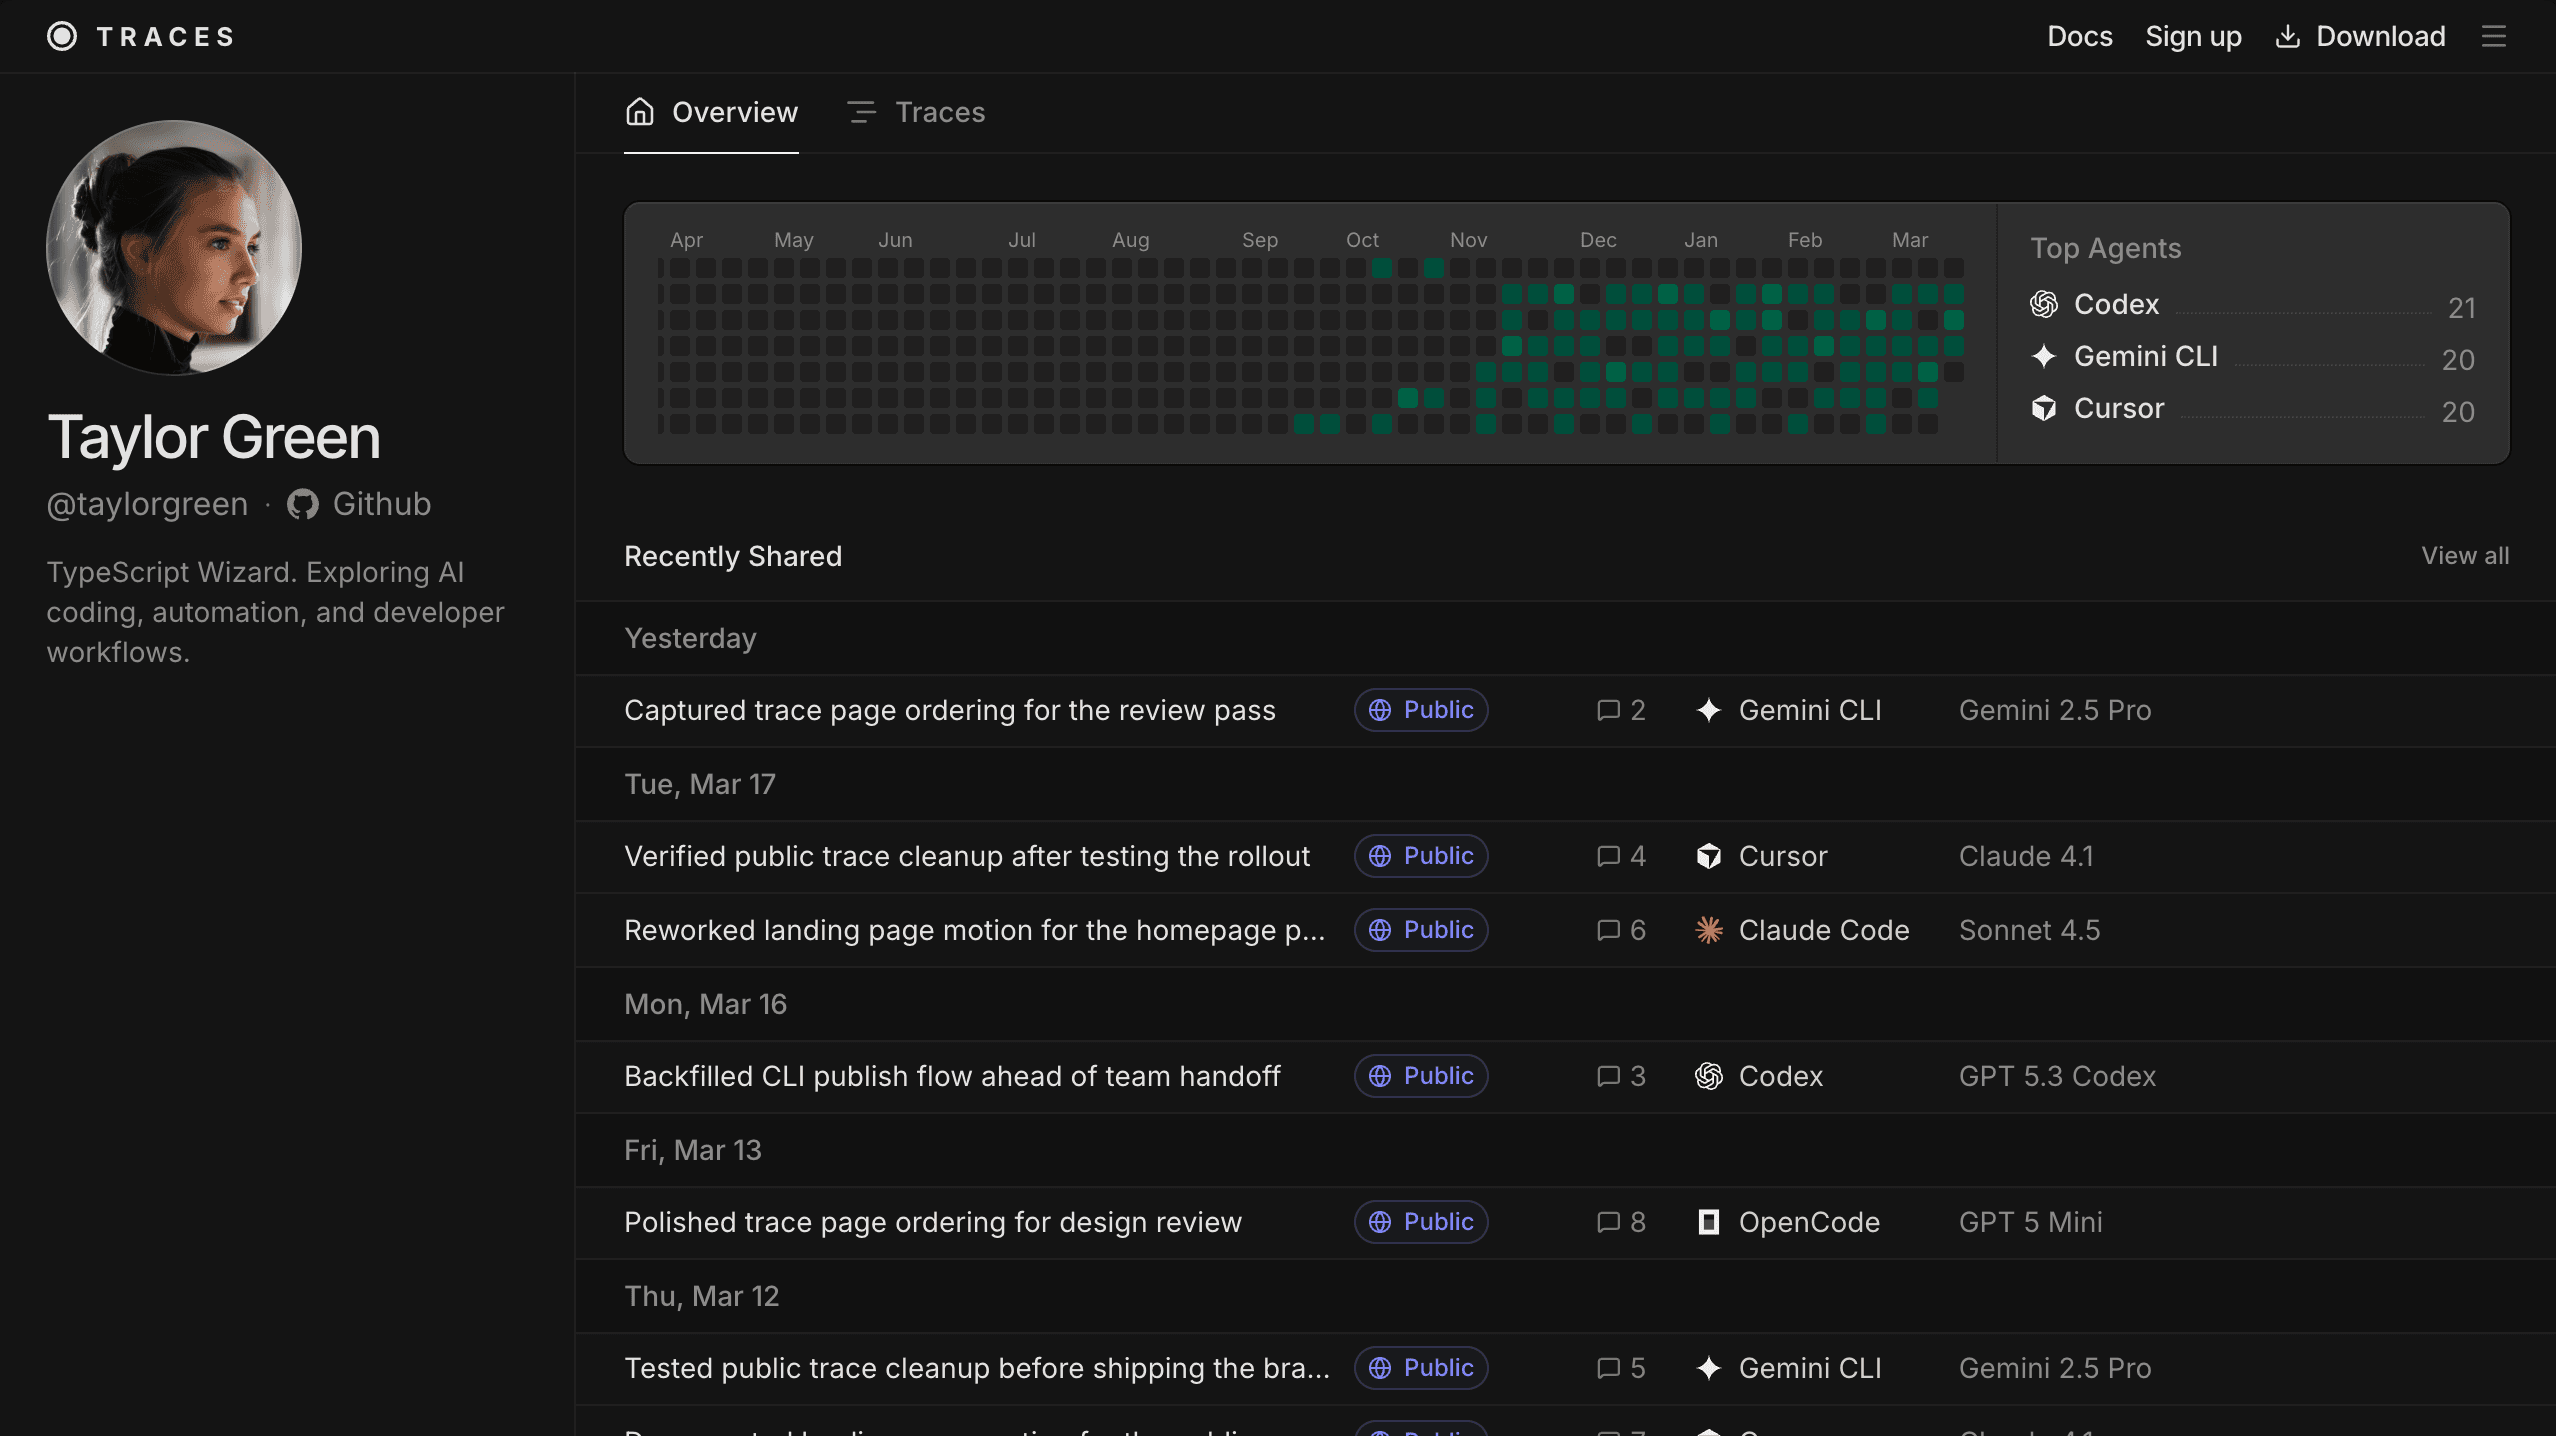
Upload from any agent
Publish traces from 10+ supported agents directly in the CLI.
Share sessions live & compound your learning.
For software developers & teams.
Works with your favourite agents


Start sharing traces from any agent, in minutes.
Publish traces from 10+ supported agents directly in the CLI.
Copy the link & share your trace with your team or the world.
UserMenu because it uses imperative WAAPI and can re-measure on state changes. I'm reading that implementation next and then I'll verify smoothing techniques from current guidance.Download a full trace or continue working on someone else's.
Download a trace, or continue it in Claude Code. The open agent menu lists Claude Code, Codex, Cline, Pi, Cursor, OpenCode, Amp, OpenClaw, GitHub Copilot, Hermes, Droid, Grok, Kimi Code, Antigravity, Prime Agent, fx, DeepSeek Harness, with Claude Code selected.
Traces for Teams
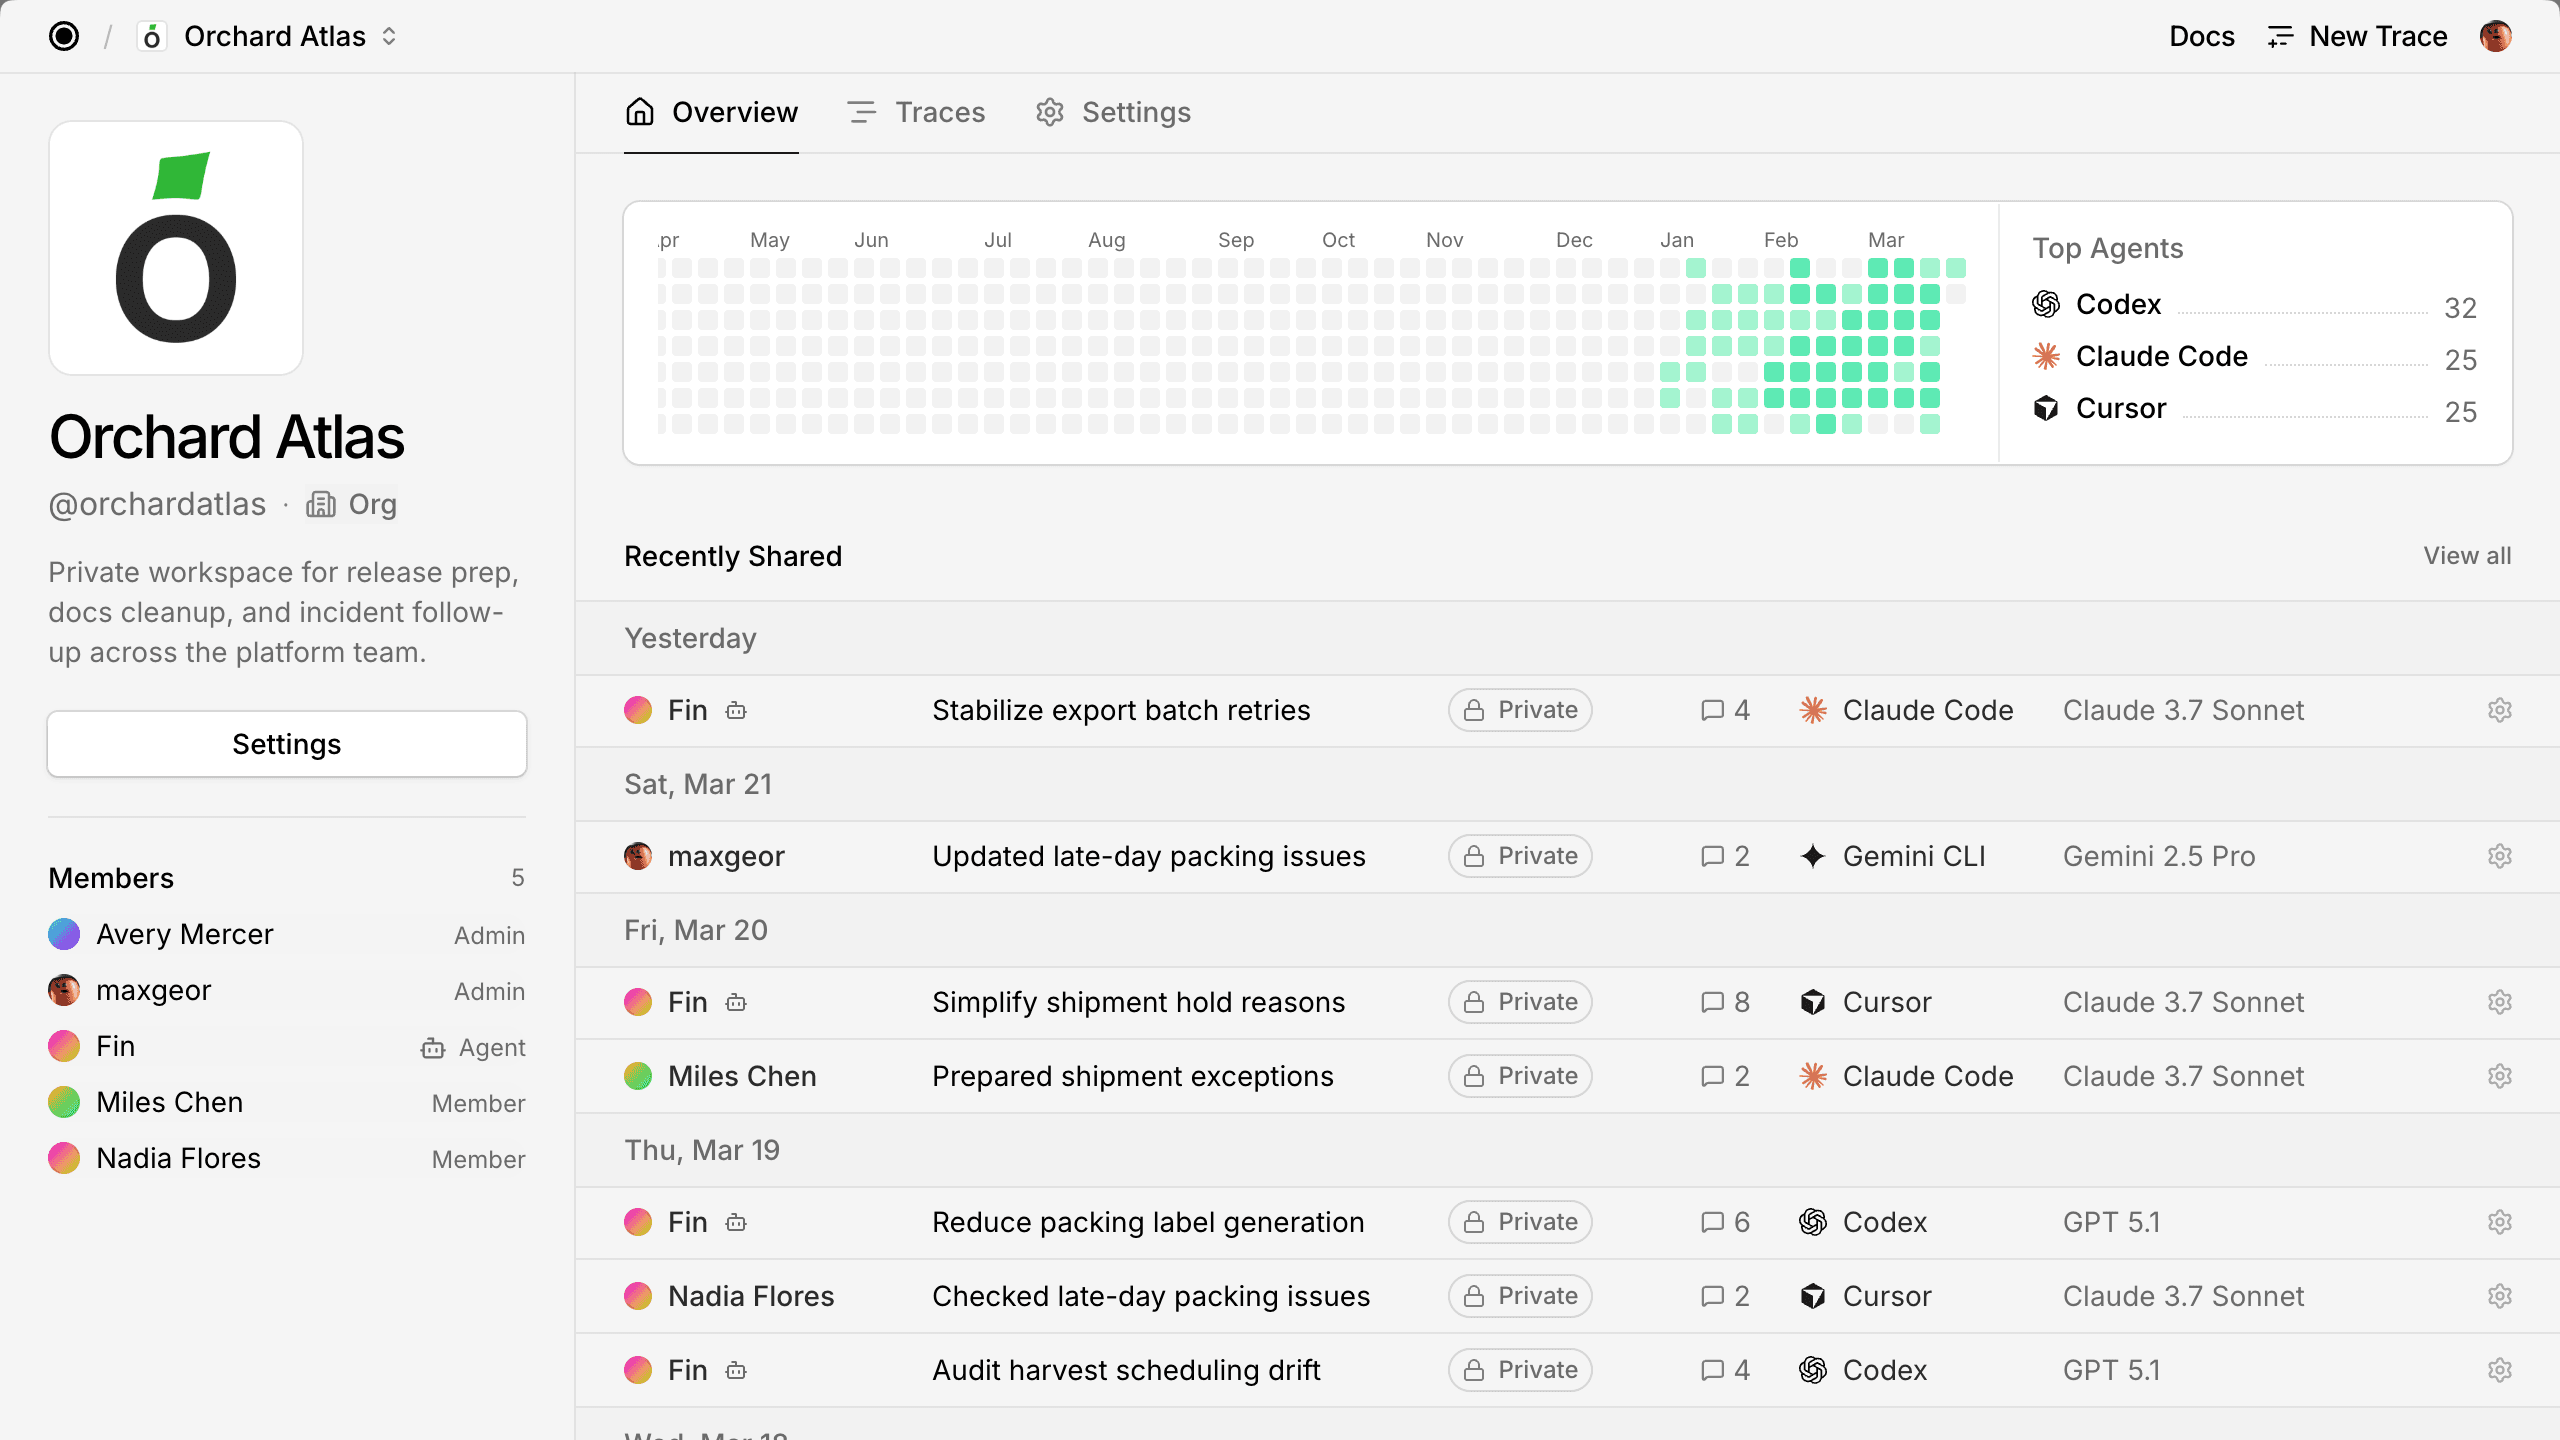
Traces gives teams one place to see work in progress, share context on finished work, and see which agents people are using.


“Github increasingly doesn't feel like the best place to understand the work done on a codebase. Agent traces provide a much more human-readable overview. Just started using traces.com. Feels quite nice.”
Millin Gabani, CEO of Worklayer
See original postShare agent conversations without worrying about sensitive data.
Share your traces privately, directly, or publicly, so only the right people see them.
maujim · 102 messages
Diagnose and Enhance Voltage Error Reporting
maujim · 102 messages
Diagnose and Enhance Voltage Error Reporting
maujim · 102 messages
Diagnose and Enhance Voltage Error Reporting
Set team-level policies to control how your team can share traces.
Traces can be published as:
We automatically strip sensitive data like API keys, emails & database credentials from traces on publish.
Shared the rollout trace after scrubbing [REDACTED], [REDACTED], and [REDACTED] from the assistant reply before sending the link to the team.
The published run keeps the reasoning intact while replacing keys, customer emails, and database URLs with clear [REDACTED] markers anyone can spot immediately.
Reviewers still understand what happened, but the sensitive values stay hidden behind [REDACTED] in every shared view.
Start simple & integrate more as you go.
Publish & manage traces directly from your terminal.
Let your agent share traces as you work.
Publish traces via API with your own tools, schedulers & workflows.
Automatically share traces on every commit from your CI/CD pipelines.
Free for individuals & small teams, flexible at scale.
Core
Free
Custom
Get in touch
See what ships, loop in the right agents, and share traces with git hooks & custom skills.
Team analytics preview showing Claude Code, Codex, Cursor, Droid, and Amp as the top agents, with an average session length of 47 minutes and 82.0 percent AI output.
A GitHub-style pull request timeline shows Maya Chen committing a docs update, a Traces bot comment with pull request trace links, two preview deployments, and a pull request mention.
Traces found for this PR:
Team member list showing Maya Chen as admin, Theo Brooks as member, Alice as the invited agent, Lina Park as member, and Ari Singh as member.

A terminal conversation showing a request to share a trace, the Traces skill that ran, and the private share link confirmation.
Great, I added back the function.
Share this trace
Skill Traces
Ran traces share --trace-id w9g0svsjx839ngt --json
Shared your trace to https://traces.com/s/w9g0svsjx839ngt as private.
Supported agents include Claude Code, Cursor, OpenCode, Codex, Pi, Amp, Cline, OpenClaw, GitHub Copilot, Hermes, Droid, Grok, Kimi Code, Antigravity, Prime Agent, fx, DeepSeek Harness.
Install the CLI to get started or make an account first.
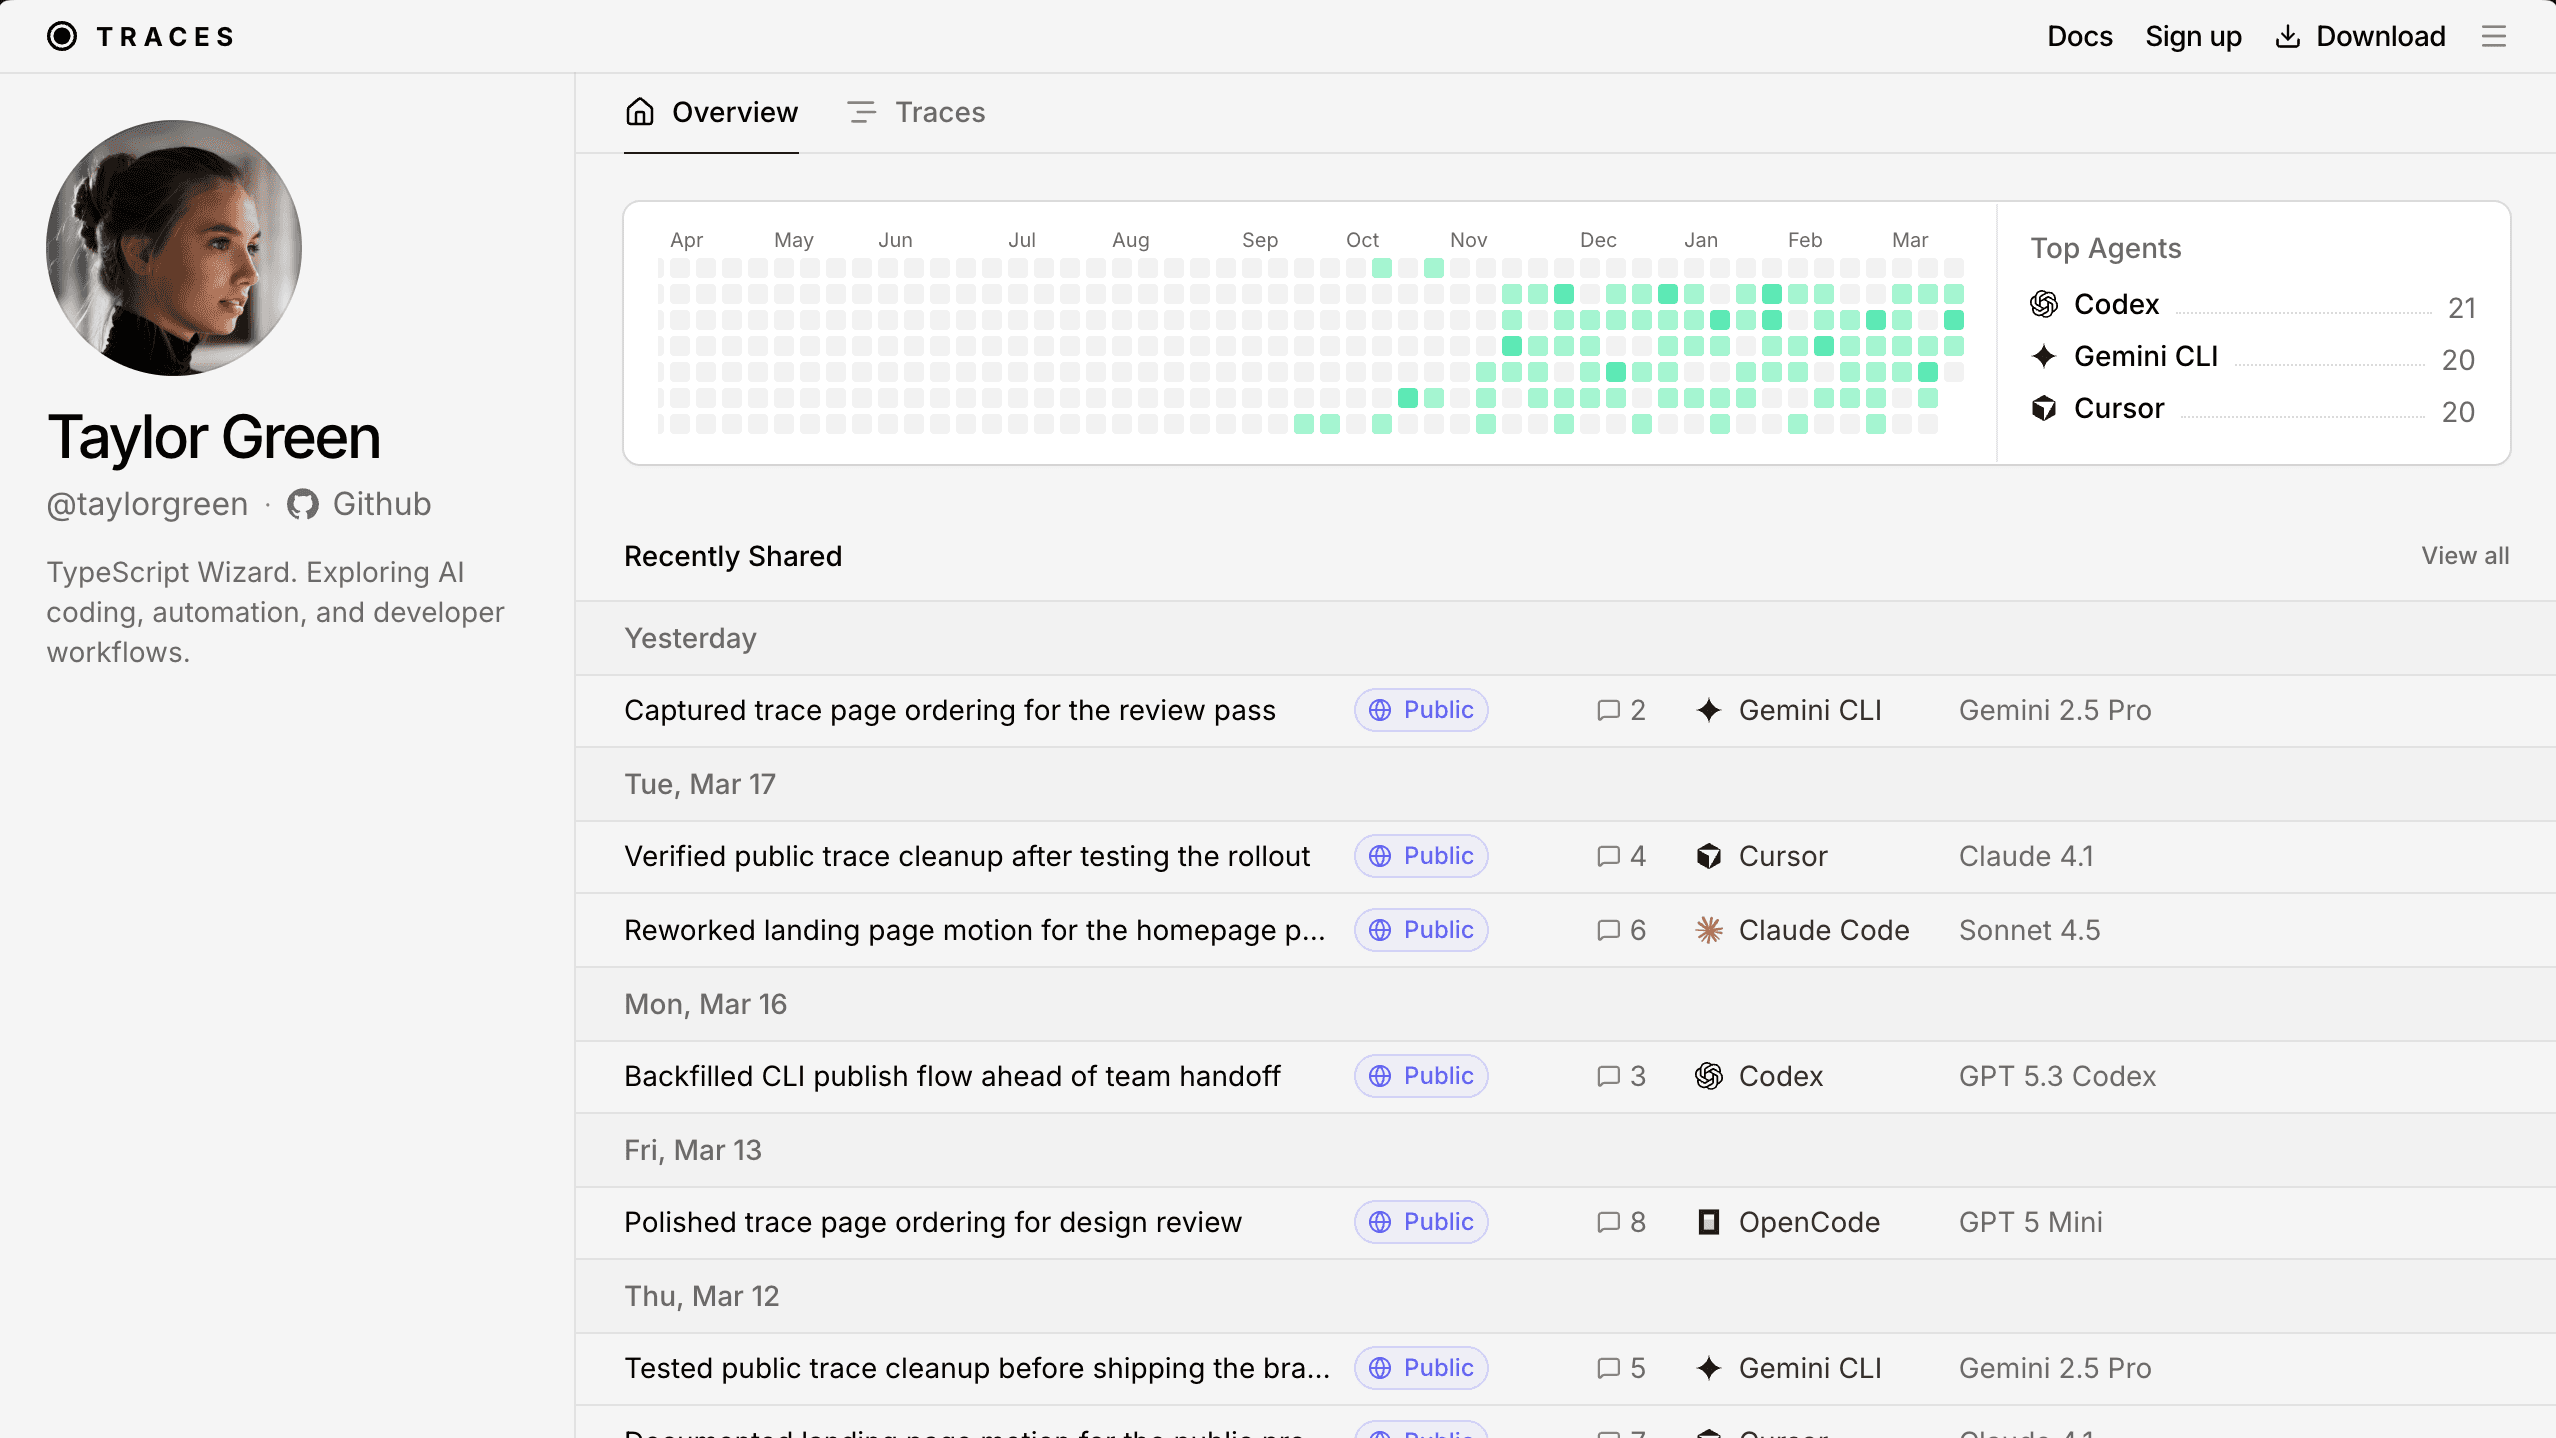
Browse traces & learn how people are using agents. Contribute by sharing your own traces.
Browse public tracesThe session involved an independent review of the entire branch 'feat/l5-meta-improvement' against the main branch. The assistant examined the full diff, verified documented invariants against the new scripts, and identified a key issue where policy metadata can disable evaluation gates due to missing validation of certain fields. The assistant also isolated the committed HEAD to ensure consistent verification results.
The user requested an independent review of the entire branch `feat/l5-meta-improvement` against `origin/main`, focusing on a new versioned improvement policy and related scripts. The assistant reviewed the full diff, ran tests, reproduced issues, and identified two key archive-integrity problems involving SHA marker forgery and round number collisions. The assistant confirmed that workflow script invocations succeeded and that GitHub's bot PR approval requirements were not treated as defects.
The user requested an independent review of the entire branch 'feat/l5-meta-improvement' against 'origin/main'. The assistant reviewed the full branch diff, reproduced measurement plans, verified policy history and dashboard accuracy, and identified a chart defect where negative validity values were incorrectly plotted as zero. The assistant also noted unsupported echo results and stale CI statuses in the backlog.
The user requested an adversarial verification of fixes in a code branch compared to the main branch, focusing on reproducing previously reported failures. The assistant inspected the code diff, ran tests, and verified most issues were fixed, but identified one issue (A3) still open regarding deduplication of error excerpts and additional minor issues found during review.
The session involved an independent review of the entire branch 'feat/l5-meta-improvement' against the main branch. The assistant examined the full diff, verified documented invariants against the new scripts, and identified a key issue where policy metadata can disable evaluation gates due to missing validation of certain fields. The assistant also isolated the committed HEAD to ensure consistent verification results.
The user requested an independent review of the entire branch `feat/l5-meta-improvement` against `origin/main`, focusing on a new versioned improvement policy and related scripts. The assistant reviewed the full diff, ran tests, reproduced issues, and identified two key archive-integrity problems involving SHA marker forgery and round number collisions. The assistant confirmed that workflow script invocations succeeded and that GitHub's bot PR approval requirements were not treated as defects.
The user requested an independent review of the entire branch 'feat/l5-meta-improvement' against 'origin/main'. The assistant reviewed the full branch diff, reproduced measurement plans, verified policy history and dashboard accuracy, and identified a chart defect where negative validity values were incorrectly plotted as zero. The assistant also noted unsupported echo results and stale CI statuses in the backlog.
The user requested an adversarial verification of fixes in a code branch compared to the main branch, focusing on reproducing previously reported failures. The assistant inspected the code diff, ran tests, and verified most issues were fixed, but identified one issue (A3) still open regarding deduplication of error excerpts and additional minor issues found during review.